Third-Party Poker Software Scandal Raises New Security Concerns for Online Players

pessi-lamm
35 minutes ago
Pessi Lamm 35 minutes ago
Share this article
Or copy link
  • High-stakes poker pros hit by a third-party software security breach.
  • Jurojin and IntuitiveTables' compromised updates let attackers remotely access player screens.
  • Incident highlights the security risks of trusted, non-official poker tools.
Jurojin and IntuitiveTables are at the center of a new online poker security scandal involving compromised third-party software.
A new online poker security scandal has raised questions about the risks of using third-party poker software, after a remote-access tool was allegedly installed on the computers of high-stakes players.

The investigation, led by cybersecurity researcher WolfSec0x0, found evidence of a covert Mesh Agent installation delivered through compromised poker software. 

The agent could give an attacker remote access to an affected Windows computer, including the ability to view the player's screen and potentially see their hole cards. 

Around 30 high-stakes players are currently believed to have been targeted.

Jurojin and IntuitiveTables Targeted

The two third-party poker tools connected to the investigation are Jurojin and IntuitiveTables.

Jurojin is a poker productivity and table-management tool offering features such as table tiling, hotkeys, bet sizing and real-time overlays. 

IntuitiveTables provides similar functionality, including table placement, hotkeys, betting controls and poker overlays.

Neither tool is a poker site. They run alongside the poker client and are used primarily by players who want to manage multiple tables more efficiently.

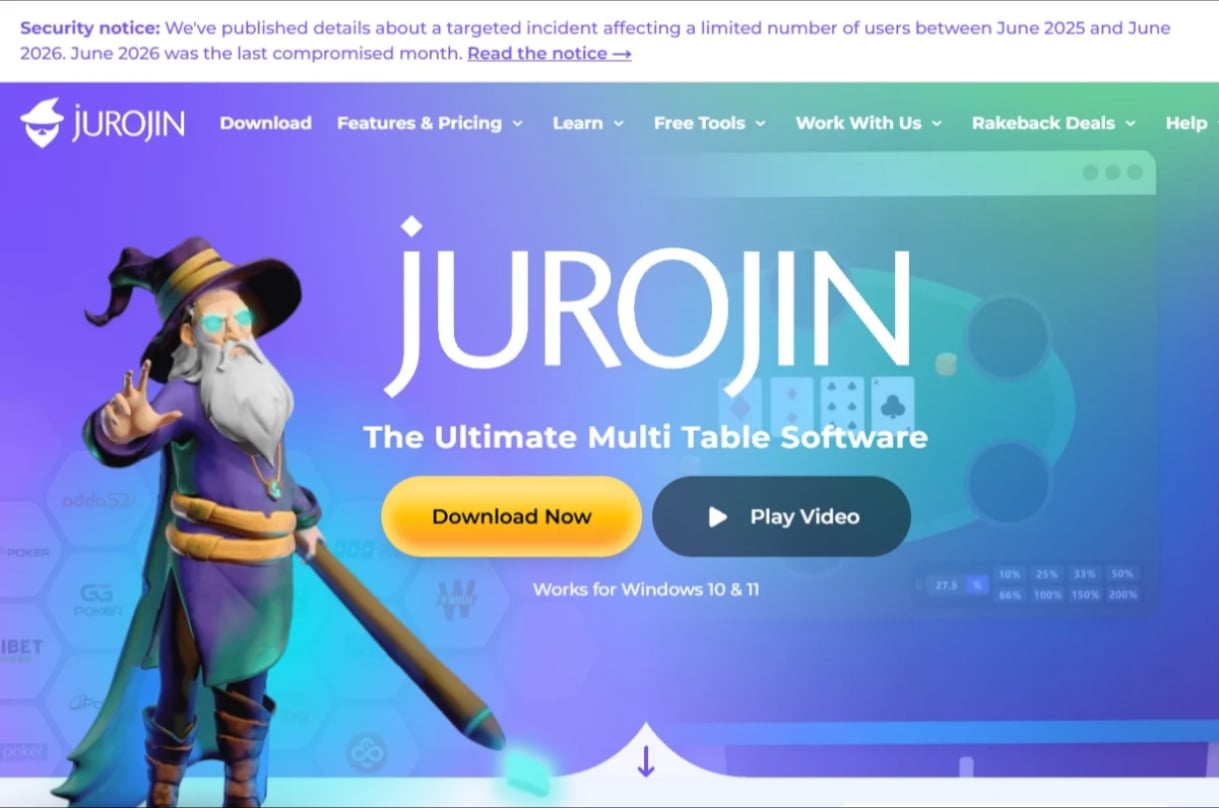
Jurojin has now confirmed that its update system was compromised. According to the company, an attacker intermittently replaced update packages delivered to a specific group of users between June 2025 and June 2026, with some compromised packages containing a remote-access tool. 

Jurojin says the attack was highly targeted rather than a mass infection.

IntuitiveTables has also confirmed that it was one of the applications targeted by the same actor.

undefined
Jurorin homepage with the security notice reporting about the incident.

Mesh Agent Provided Remote Access

The remote-access component identified in the investigation was Mesh Agent, part of MeshCentral, a legitimate open-source remote-management platform.

MeshCentral itself is not malware. The problem is how the software was allegedly deployed and used in this case.

According to the investigation, the agent could provide remote screen access, mouse and keyboard control, access to files and other information on the affected computer. That creates an obvious problem when the machine is being used to play online poker.

The player's hole cards are sitting right there on the screen.

No access to the poker site's servers is necessarily required.

Poker Sites Were Not The Entry Point

One of the more important details is that the investigation has not identified a poker site's own software as the source of the compromise. The reported attack went through third-party software installed on players' computers instead. 

PokerStrategy reports that the poker sites themselves were not compromised, while WolfSec0x0 specifically stated that GGPoker and ClubWPT Gold were not involved.

That creates a different type of security problem for online poker.

Poker operators can secure their own clients and servers, but players increasingly use additional software alongside those clients. Table managers, HUDs, trackers and hotkey tools have become a normal part of the online poker ecosystem.

If one of those trusted tools is compromised, the potential security problem can move with the player into the poker table.

The 30 Players May Not Be The Only Concern

The approximately 30 targeted players are the obvious victims in this case.

But there is a potentially wider issue.

If an attacker can remotely view the screen of a compromised player while that player is involved in a real-money game, the information could potentially be used against the other players at the table.

Those opponents don't need to have the compromised software installed. They don't need to know anything unusual is happening.

They only need to be sitting across the table from the affected account.

There is currently no complete public list of affected games or hands, so it is impossible to determine how many other players may have been exposed or whether specific accounts actually used stolen hole-card information.

That distinction matters.

What has been uncovered is a potential security threat created by compromised third-party poker software, rather than evidence that every player using external tools is cheating.

A New Problem for Online Poker

The incident is another reminder that online poker security does not end with the poker client.
Jurojin says it has strengthened security around its update infrastructure, including additional controls over sensitive configurations and download logging. The company has also contacted users it believes were affected.

For players, the incident raises a less comfortable question. 

How much trust should be placed in software that sits directly alongside the poker client and interacts with the tables?

That question now goes beyond the roughly 30 players whose computers were allegedly targeted.
It potentially concerns everyone sitting at the same table. 

One weak link can ruin it for everybody.

More Poker News

Upcoming Events